What will I learn?
- What is an endpoint?
- Endpoint management - An overview
- Types of endpoint management
- Why is endpoint management important?
- How does endpoint management work?
- Endpoint management vs. Unified endpoint management
- Endpoint management vs. Endpoint security
- Common endpoint management policies
- Endpoint management in workplace software
- Endpoint management examples
What is Endpoint Management?
Endpoint management refers to how organizations discover, govern, and protect all of the devices that access their network through a centralized system of policies and controls. As organizations expand across distributed work environments, the number of these devices has grown significantly. Today, an organization’s IT infrastructure extends to every laptop, mobile phone, tablet, and connected device in use, and each of these devices carries its own security risk.
Managing these devices consistently and securely is what endpoint management is built to address. This article covers the core concepts and types of endpoint management, its significance in IT security, and how it applies within modern workplace suite software.
What is an endpoint?
An endpoint is any device that connects to an organization’s network or accesses its digital resources. In a workplace context, an employee’s work laptop, a shared office printer, or a mobile phone configured to access corporate email all qualify as endpoints.
Each endpoint represents a point of access to organizational data and systems. The broader the device landscape, the larger the potential attack surface.
Endpoint management - An overview
Endpoint management refers to the set of processes and tools used by IT administrators to monitor, configure, and maintain all of the devices connected to an organization’s network from a centralized system.
In practice, it serves as the operational backbone of an organization’s IT infrastructure. Every device that connects to a corporate network introduces a potential point of vulnerability. Endpoint management gives IT teams the means to govern these devices systematically, rather than reacting to issues as they arise.
Its scope extends across the entire device lifecycle. It begins the moment a device is enrolled into the system. It then continues through configuration, maintenance, and security enforcement, all the way to decommissioning. At each stage, the goal remains the same: Ensure that every device meets the organization’s security and operational standards.
Organizations today manage a mix of laptops, mobile phones, tablets, servers, and IoT devices. These devices are often spread across multiple locations and operating systems. A centralized endpoint management system brings all of them under a single point of control. This enables consistent policy enforcement and a clear, real-time view of every device on the network.
Types of endpoint management
Mobile Device Management (MDM)
MDM provides IT administrators with control over mobile devices at the device level. It gives administrators the ability to bring devices into the system, define how they operate, and disable or clear a device when necessary.
MDM is typically used in organizations with a mobile-centric or field-based workforce. Its scope is limited to the device itself and doesn’t extend to managing applications or data independently.
Enterprise Mobility Management (EMM)
EMM extends MDM by adding application-level and data-level controls. A key capability of EMM is containerization, the technical separation of work data from personal data on the same device. This allows IT to remove corporate data selectively without affecting personal content, making EMM well-suited for BYOD environments.
Unified Endpoint Management (UEM)
UEM consolidates the management of all endpoint types—like mobile devices, laptops, desktops, printers, wearables and IoT—under a single platform with a unified policy engine. It’s the most comprehensive approach and is increasingly adopted by organizations managing mixed-device environments across multiple operating systems.
Endpoint Detection and Response (EDR)
EDR is focused on threat detection and incident response rather than device management. It monitors endpoint activity in real time, identifies anomalous behavior, and enables rapid response to security incidents. EDR is commonly deployed alongside MDM or UEM as a dedicated security layer.
Why is endpoint management important?
Endpoints are among the most frequently targeted entry points in cybersecurity incidents. From a compliance standpoint, regulations such as GDPR and HIPAA require organizations to maintain demonstrable control over how data is accessed and stored across devices. Endpoint management provides the audit trails, access controls, and policy documentation needed to meet these requirements.
Operationally, endpoint management also supports IT workflows around employee onboarding and off boarding. When staff join, devices are provisioned correctly and on time. When they leave, access is revoked completely, with no loose ends.
Understanding why endpoint management matters comes down to four areas: security, compliance, operational efficiency, and visibility and control. Each plays a distinct role in how organizations protect and manage their device landscape.
Security
Without endpoint management, there’s no reliable way to verify that devices connecting to corporate systems are running updated software, are free from malware, or haven’t been tampered with. It enforces security baselines across all devices, ensuring that patches are applied consistently, access is limited to verified devices, and any device that poses a risk can be isolated or wiped promptly.
Compliance
Regulations such as GDPR and HIPAA require organizations to demonstrate control over how data is accessed and stored across devices. Endpoint management supports this through audit trails, access controls, and policy documentation needed to establish regulatory alignment, particularly in data-sensitive industries like healthcare, finance, and legal.
Operational efficiency
Endpoint management directly supports IT workflows around onboarding and offboarding. It automates device provisioning for new employees and ensures that access is revoked completely when someone leaves, reducing manual dependency and the risk of oversight on both ends.
Visibility and control
IT teams cannot secure what they cannot see. Endpoint management provides a real-time view of every connected device, its compliance status, software version, and access history, enabling early detection of anomalies and faster incident response. This visibility is especially critical in remote and BYOD-heavy environments where physical oversight isn’t possible.
How does endpoint management work?
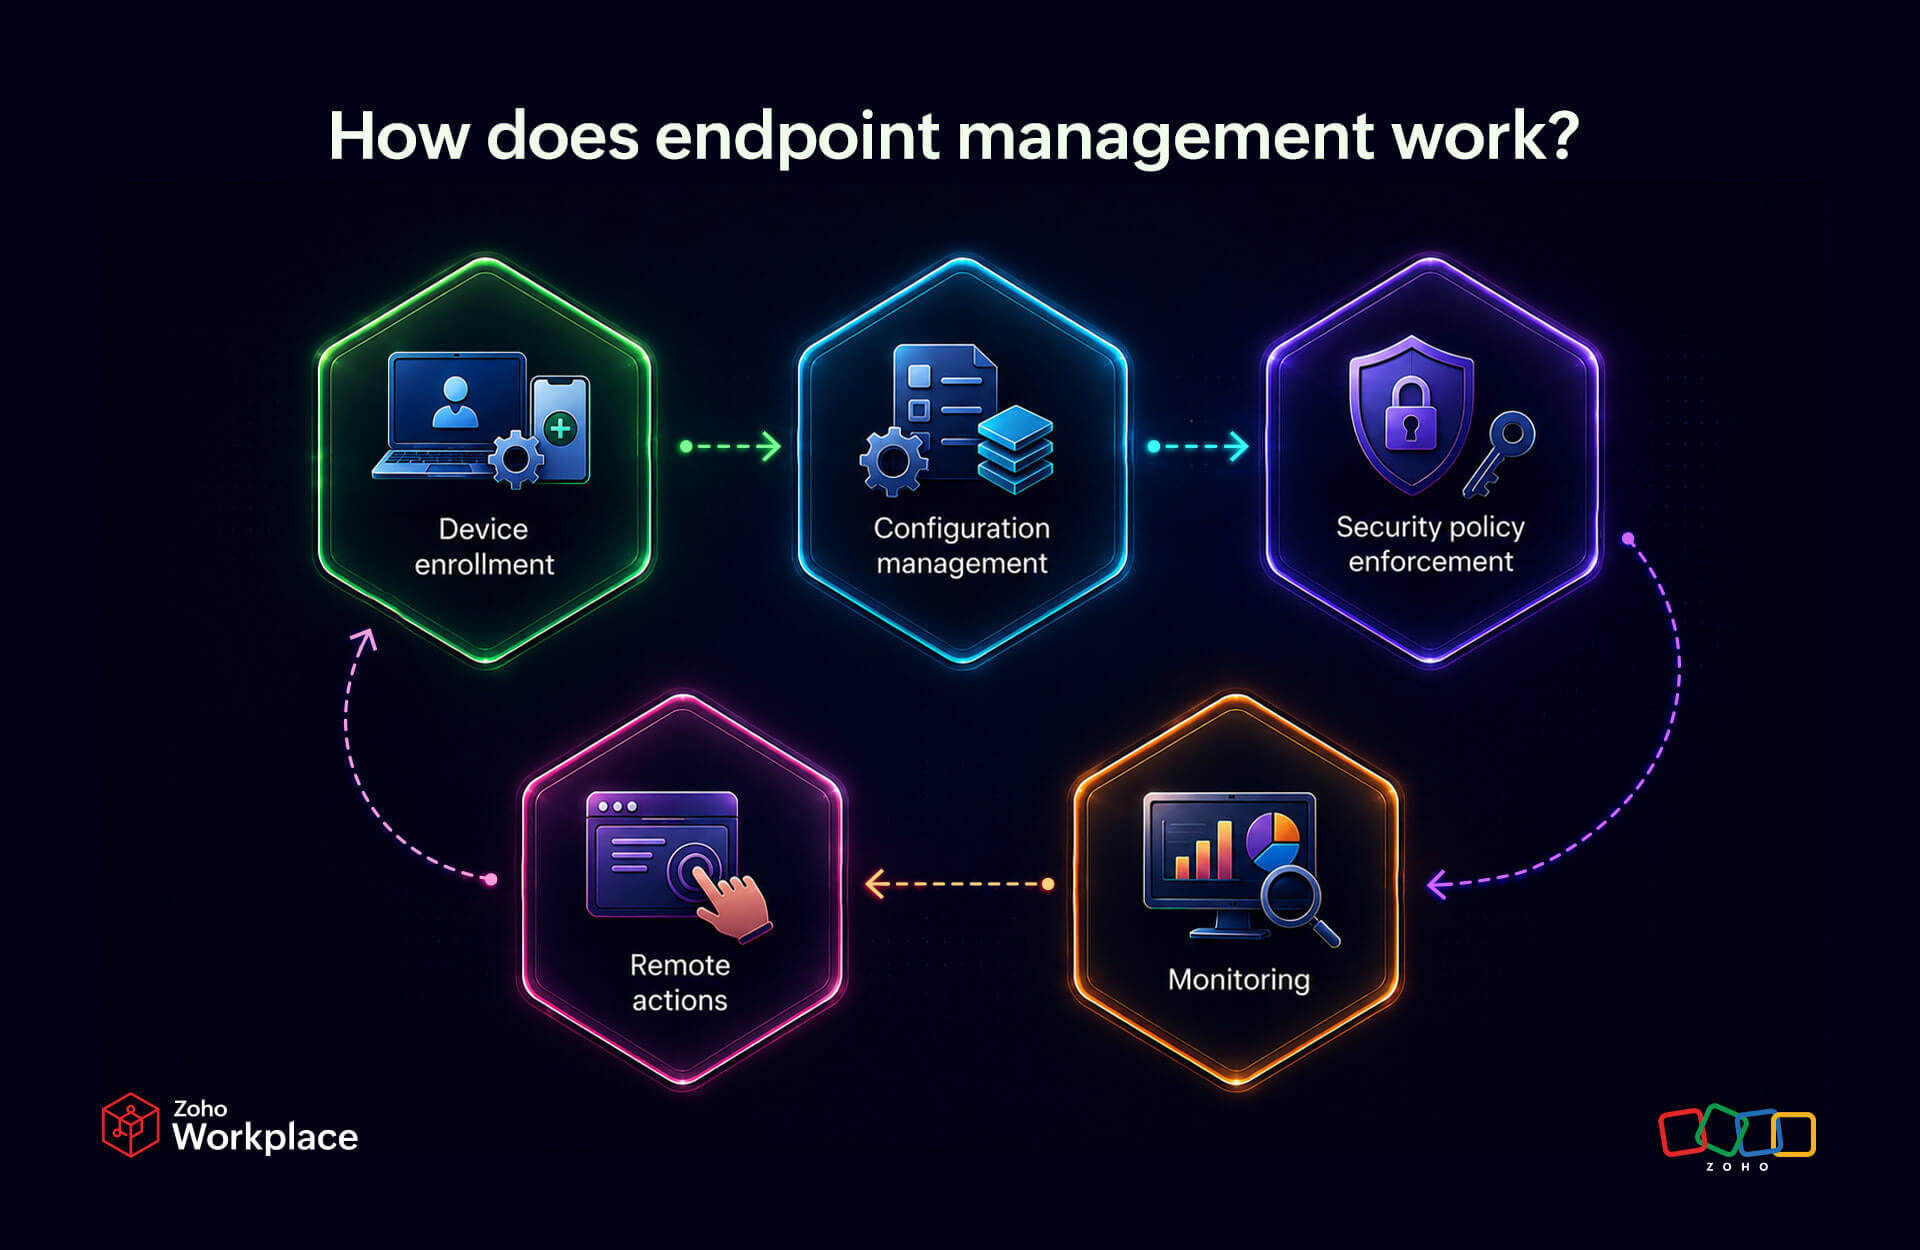
Understanding how endpoint management works comes down to the core functions it performs. These functions don’t operate in isolation, but they work together as a continuous process, each one building on the last. Together, they cover everything from the moment a device joins the network, through its day-to-day operation, to the actions taken when something goes wrong.
Device enrollment
Device enrollment is the process of bringing a device under organizational control by registering it into the endpoint management platform. Enrollment can be done manually by the user or automatically when a device connects to the network. It can also happen through zero-touch provisioning, where a device is pre-configured by the manufacturer and ready to use straight out of the box. Once enrolled, the device becomes visible to IT administrators and subject to the organization’s policies.
Configuration management
Configuration management involves applying and maintaining standardized settings across all enrolled devices. This includes defining which applications are installed, how the device connects to the network, and what users can or cannot do on the device. When a new policy is introduced or updated, the change is pushed consistently across all relevant devices, without manual intervention on each one. For large organizations managing hundreds or thousands of devices, this level of automation is essential to maintaining uniformity.
Security policy enforcement
Security policy enforcement ensures that all devices meet a defined set of security standards before and during network access. This includes pushing software and OS updates to address known vulnerabilities. It also covers enforcing password and encryption requirements, restricting access to unauthorized applications, and managing user permissions based on role.
Monitoring
Monitoring involves the continuous tracking of device activity, health, and compliance status across the device fleet. IT administrators can view which devices are active, what applications are running, and whether security policies are being followed. Any unusual behavior can be flagged early. In remote and BYOD environments, this real-time visibility is the primary means through which IT teams maintain oversight of devices they cannot physically access.
Remote actions
Remote actions refer to operations performed on a device from a distance, without physical access to it. Common examples include locking a device to prevent unauthorized use, wiping it entirely to protect sensitive data, or selectively removing only corporate content while leaving personal files intact. These actions are typically triggered when a device is reported missing, stolen, or flagged as a security risk.
In addition to security, endpoint management covers device provisioning, regulatory compliance, and lifecycle management, from initial setup through to secure decommissioning.
Endpoint management vs. Unified endpoint management
Endpoint management is an IT discipline that covers how organizations govern, maintain, and protect every device that connects to their network. It encompasses the processes, policies, and tools used to manage those devices, regardless of type or platform.
Unified Endpoint Management, or UEM, is a specific approach within that broader practice. It refers to the use of a single platform to manage all endpoint types—like laptops, desktops, mobile devices, tablets, IoT devices, and wearables—under one unified policy engine.
The key distinction is consolidation. Traditional endpoint management often involves separate tools for different device types. One system handles desktops, another handles mobile devices, and so on. UEM eliminates that fragmentation. Everything is brought under one console, managed through a single set of policies.
Endpoint management | Unified endpoint management | |
| Scope | Broad practice covering all device governance | A specific platform-based approach |
| Tools | May involve multiple separate tools | A single consolidated platform |
| Device types | Varies by tool | All device types in one place |
| Best suited for | Any organization managing devices | Organizations with mixed, complex device environments |
Endpoint management vs. Endpoint security
These two terms are closely related but serve different purposes. Confusing them is common. Understanding the distinction matters for building a complete IT strategy.
Endpoint management concerns the administration and operational control of devices. Its focus is on keeping devices configured correctly, up to date, compliant with policies, and functioning as expected.
Endpoint security deals exclusively with defending devices against external and internal threats. Its focus is on preventing, detecting, and responding to cyberattacks, malware, unauthorized access, and data breaches.
In practice, the two overlap significantly. A well-implemented endpoint management system will include security features. Endpoint security tools are often deployed and managed through endpoint management platforms. Neither replaces the other. Together, they form a complete approach to device governance.
Endpoint management | Endpoint security | |
| Primary focus | Device administration and operations | Threat prevention and response |
| Key functions | Enrollment, configuration, patching, monitoring | Antivirus, encryption, threat detection, incident response |
| Goal | Devices are compliant and operational | Devices are protected from threats |
| Relationship | Broader discipline | A component within endpoint management |
Common endpoint management policies
Endpoint management policies establish the boundaries within which devices operate, specifying what’s permitted, what’s restricted, and what security standards must be met. They’re configured in the management system and applied automatically across all enrolled devices.
Password and authentication policy
Defines minimum password length, complexity requirements, expiry intervals, and whether multifactor authentication is mandatory. This policy ensures that access to devices and systems is protected by more than just a simple password.
Device encryption policy
Requires that data stored on enrolled devices is encrypted. This protects sensitive information in the event a device is lost or stolen, ensuring that data cannot be accessed without the correct credentials.
Software update and patch policy
Specifies how and when software updates and security patches are deployed across devices. It defines which patches are critical, the acceptable timeframe for deployment, and how exceptions are handled.
Application control policy
Determines which applications are permitted or restricted on enrolled devices. Unauthorized or potentially harmful applications can be blocked from installation, reducing the risk of malware and data leakage.
Access control policy
Governs which users and devices are permitted to access specific resources, systems, or data. Access is typically assigned based on role, ensuring that employees can only reach what’s relevant to their function.
Remote wipe policy
Defines the conditions under which a device can be remotely wiped or locked, such as when it’s reported lost, stolen, or when an employee exits the organization. In BYOD scenarios, this policy may also include selective wipe, which removes only corporate data.
BYOD policy
Sets the rules for personal devices used for work purposes. This includes minimum security requirements a personal device must meet before being granted access to corporate resources, and the boundaries of what the organization can and cannot manage on the device.
Endpoint management in workplace software
Workplace suites, platforms that consolidate email, file storage, messaging, and collaboration tools, all handle a significant volume of organizational data. Most modern workplace suites include native endpoint management capabilities or integrate with dedicated endpoint management solutions to control device access.
Google Workspace includes built-in endpoint management that allows administrators to enforce device passcodes, manage app distribution, and remotely wipe specific accounts across Android, iOS, and Windows devices. It supports agentless management, meaning no additional software installation is required on the user’s device.
Microsoft 365 integrates with Microsoft Intune for device lifecycle management, and with Microsoft Defender for endpoint threat protection. It supports conditional access policies, allowing organizations to restrict resource access based on device compliance status. This makes it a common choice in regulated industries such as healthcare, finance, and legal.
Apple’s ecosystem, managed through Apple Business Manager and MDM profiles, allows IT administrators to control how devices interact with business applications. It covers encryption enforcement, app management, and remote wipe capabilities across Apple devices used with iWork and other business tools.
Dedicated endpoint management platforms, such as ManageEngine Endpoint Central, operate as standalone solutions, independent of any specific workplace suite. They support a broad range of operating systems including Windows, macOS, Linux, Android, iOS, ChromeOS, and tvOS, making them applicable across diverse device environments.
Core capabilities typically include device onboarding, patch management, software deployment, asset tracking, vulnerability assessment, and remote troubleshooting. On the security side, these platforms cover application control, browser security, peripheral device control, data loss prevention, and malware protection. All of this is managed from a single centralized console, addressing the full device lifecycle from enrollment through to decommissioning.
Across these platforms, endpoint management functions as a standard component of access governance rather than an optional feature.
Endpoint management examples
The following scenarios illustrate how endpoint management functions in real workplace situations.
New employee onboarding
When a new employee joins an organization, their device needs to be configured with the right applications, access permissions, and security settings. Through zero-touch provisioning, the device can arrive pre-configured and ready to use. The IT team doesn’t need to handle it manually. Policies are applied automatically upon enrollment.
Remote worker access
An employee working from home connects to the corporate network on a personal laptop. The endpoint management system checks whether the device meets the organization’s compliance requirements. This includes running an approved OS version and having encryption enabled. If the device doesn’t meet these requirements, access is restricted until it’s brought into compliance.
Lost or stolen device
An employee reports their work phone missing. The IT administrator remotely locks the device immediately, preventing unauthorized access. If the device isn’t recovered, a remote wipe is initiated. Corporate data is purged from the device remotely, regardless of where the device is located.
Software vulnerability response
A critical security vulnerability is identified in a widely used application. The endpoint management system automatically deploys the relevant patch to all affected devices. The vulnerability is closed before it can be exploited, with no manual updates required on individual devices.
Employee exit
When an employee leaves the organization, their access to all corporate systems and applications is revoked immediately. This is done through the endpoint management platform. On a personal device, a selective wipe removes all corporate data while leaving personal files intact.
BYOD compliance enforcement
Where personal devices are sanctioned for work use, the BYOD policy defines the minimum security standards they must meet before being granted access to corporate resources. The endpoint management system enforces a minimum set of security requirements on all enrolled personal devices. These include screen lock, encryption, and approved app restrictions. Personal content on the device remains untouched.
FAQ
What is an endpoint?
An endpoint is any device that connects to an organization’s network or accesses its digital resources. This includes laptops, desktops, smartphones, tablets, printers, servers, and IoT devices.
Why is endpoint management important?
Endpoints are among the most frequently targeted entry points in cybersecurity incidents. Endpoint management protects against threats, ensures regulatory compliance, supports operational efficiency, and gives IT teams real-time visibility across all connected devices.
What are examples of endpoints?
Common examples include an employee’s work laptop, a mobile phone configured to access corporate email, a shared office printer, a tablet used in the field, and IoT devices connected to the corporate network.
What is endpoint management?
Endpoint management is the practice of bringing every device connected to an organization’s network under centralized oversight. It covers the full device lifecycle, from enrollment and configuration through to monitoring, security enforcement, and decommissioning.
What is the difference between endpoint management and endpoint security?
Endpoint management focuses on the administration and operational control of devices, keeping them configured, updated, and compliant. Endpoint security is the practice of safeguarding devices from cyberthreats, including malware, unauthorized access, and data breaches.
What is the difference between MDM and UEM?
MDM operates at the device level, giving IT administrators control over mobile device enrollment, configuration, and remote actions such as lock and wipe. UEM is a broader approach that manages all endpoint types, laptops, desktops, mobile devices, IoT, and wearables from a single unified platform.
What is endpoint management software used for?
Endpoint management software is used to enroll and configure devices, enforce security policies, deploy software updates and patches, monitor device activity and compliance, and perform remote actions such as locking or wiping devices when needed.
How does endpoint management support remote work?
Endpoint management enforces consistent security policies on devices regardless of location. It allows IT teams to monitor device health, restrict access from non-compliant devices, and perform remote actions, such as locking or wiping a device, without physical access to it.
What are common endpoint management policies?
Common policies include password and authentication requirements, device encryption, software update and patch schedules, application control, access control based on user role, remote wipe conditions, and BYOD rules for personal devices used at work.
Is EDR the same as endpoint management?
No. EDR, or Endpoint Detection and Response, focuses specifically on detecting and responding to security threats in real time. Endpoint management is a broader practice that covers device administration, configuration, compliance, and lifecycle management. EDR is commonly deployed as a dedicated security layer alongside endpoint management tools.